The Digital Operational Resilience Act (DORA) writes training into law twice. Article 13(6) makes ICT security awareness programmes and digital operational resilience training compulsory modules in staff training schemes, for all employees and senior management. Article 5(4) separately requires members of the management body to keep the knowledge and skills needed to understand and assess ICT risk up to date, including through regular, specific training. Most programmes discover both requirements late, usually when a review asks for the completion records. This guide sets out who is in scope, what the two obligations demand, and the evidence that answers the question.
Two obligations, two legal bases
Article 13(6) sits in the learning chapter of Pillar 1. It requires financial entities to develop ICT security awareness programmes and digital operational resilience training, and to embed them as compulsory modules in their staff training schemes. The scope is explicit: the programmes apply to all employees and to senior management staff, with a level of complexity commensurate to the remit of their functions. Where appropriate, ICT third-party service providers are included in the relevant training schemes too.
Article 5(4) belongs to governance. Members of the management body must actively keep up to date sufficient knowledge and skills to understand and assess ICT risk and its impact on the entity’s operations, including by following specific training on a regular basis, commensurate to the ICT risk being managed. This is not the staff module dressed up for directors: it is a separate duty attached to the accountability the management body carries under Article 5.
Who is in scope
| Population | Legal basis | What commensurate looks like |
|---|---|---|
| All employees | Art. 13(6) | Baseline awareness: recognising and escalating ICT incidents, security hygiene, each person’s role when a disruption starts |
| Senior management staff | Art. 13(6) | The baseline plus the decisions their remit carries: prioritisation, communication, continuity trade-offs |
| Management body members | Art. 5(4) | Specific training, on a regular basis, sized to the entity’s ICT risk profile: enough to challenge the framework they approve |
| ICT third-party service providers | Art. 13(6) with Art. 30(2)(i) | Where appropriate: participation in your relevant programmes, with the conditions set in the contract |
Entities under the simplified ICT risk management framework are not exempt either. Article 16(1)(h) asks them to develop ICT security awareness programmes and digital operational resilience training for staff and management, according to their needs and ICT risk profile.
What “compulsory modules” changes
The wording matters. A voluntary lunchtime webinar with a sign-up sheet is not a compulsory module in a staff training scheme. The scheme itself, the document that governs what every employee must complete, has to carry the DORA modules. Three things follow mechanically: new joiners receive them, completion is tracked per person, and non-completion is visible to someone whose job is to chase it.
On frequency, DORA fixes no number for staff training. For the management body it sets a standard, “on a regular basis”, without defining it. The defensible implementation is a cadence written into the training policy, applied, and evidenced. What does not survive review is training that ran once, at go-live, for the people who happened to be employed that year.
Why the board obligation is separate
Article 5(2) makes the management body define, approve, oversee and answer for the implementation of the ICT risk management framework. Article 5(4) is what makes that plausible: a body that cannot assess ICT risk cannot meaningfully approve an ICT risk framework. That is why board training records are a natural early request in any supervisory conversation about governance, and why they deserve their own log: date, topic, provider, duration, attendee. Board-level reporting follows the same evidential logic; the DORA board pack templates cover the reporting half of Article 5.
Who funds it: a board decision on record
Article 5(2)(g) makes the management body allocate and periodically review the appropriate budget for the entity’s digital operational resilience needs, and names these programmes explicitly: “including relevant ICT security awareness programmes and digital operational resilience training referred to in Article 13(6), and ICT skills for all staff”. The training budget is therefore not an HR line item that happens to exist. It is a decision the management body takes and reviews, and a review can ask to see it.
Your providers, your training scheme
Article 30(2)(i) carries training into the contractual provisions: the contract sets the conditions for the ICT third-party service provider’s participation in your ICT security awareness programmes and digital operational resilience training, in accordance with Article 13(6). Two practical consequences: decide which providers and which modules are appropriate before the clause is negotiated, and make sure the clause enters the contract during repapering rather than as a later amendment nobody owns.
The evidence a competent authority can ask for
- The training policy or scheme naming the DORA modules as compulsory, with an owner and a cadence.
- The role matrix: which population receives which module, and why that depth matches their remit.
- Completion records per person, including senior management, current for the present cycle.
- The management body training log under Article 5(4), showing regularity rather than a single session.
- The provider participation clause and, where exercised, the participation record.
- The triggers that force a refresh outside the cadence: a significant incident, a framework change, a new role.
Build the programme: five gestures
- Inventory the populations. Staff, senior management, management body, and the providers you will designate as appropriate. Each gets a named remit, because remit is what commensurate is measured against.
- Assign modules by remit. A baseline for everyone; deeper modules for IT and security operations, for the legal and procurement staff who negotiate Article 30 clauses, and for incident and continuity teams; a specific programme for the management body.
- Write the modules into the training scheme as compulsory. This single edit is what turns training from an initiative into evidence.
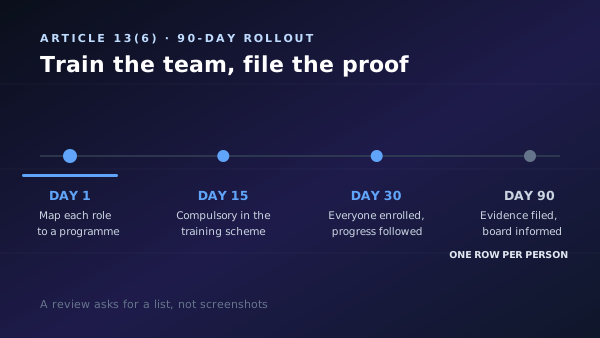
- Record completion per person and keep it exportable. The reviewer wants a list, not screenshots.
- Feed lessons back. After a significant incident or a framework change, update the modules. Article 13 is a learning chapter; the training programme is one of the things it expects to learn.
Where certification fits
DORA never requires a certificate; it requires training that happened and can be shown. A verifiable certificate is simply the cleanest per-person evidence there is: a name, a score, a date and an identifier anyone can check. Our role-based programmes map onto the populations above.
| Population | Starting certification | Legal anchor |
|---|---|---|
| Everyone, as the baseline | DORA Fundamentals Certification (free) | Art. 13(6) |
| IT, infrastructure and security | DORA for IT & Security Teams | Art. 13(6) |
| Software engineering, DevOps, platform | DORA for Developers & DevOps | Art. 13(6) |
| Legal, contracts, procurement | DORA for Legal & Contract Teams | Art. 13(6), Art. 30 |
| Compliance and risk | DORA Compliance Officer Certification | Art. 13(6) |
| Internal audit | DORA Internal Auditor Certification | Art. 13(6) |
| Management body | DORA for Boards & Executives | Art. 5(4) |
| Staff of ICT providers, where appropriate | DORA for ICT Providers & Vendors | Art. 13(6), Art. 30(2)(i) |
For a whole team, every course, track and the Masterclass is also sold as a team licence, from two seats, with a price per seat that falls as the team grows. One manager assigns and reassigns the seats, follows progress and exam results, and exports exactly the per-person completion record listed above; payment is by card or by bank transfer against a purchase order. Our 90-day rollout plan walks through the deployment step by step. Law firms advising on these contracts have their own page: DORA training for lawyers and law firms, and the full catalogue is on the DORA certification page.
Frequently asked questions
Is training mandatory under DORA?
Yes, twice over. Article 13(6) makes ICT security awareness and digital operational resilience training compulsory modules in staff training schemes, for all employees and senior management. Article 5(4) separately obliges management body members to maintain their ability to understand and assess ICT risk, including through regular specific training.
How often must DORA training run?
DORA sets no numeric frequency. For the management body it requires training “on a regular basis”. The defensible implementation is a cadence defined in your training policy, applied and evidenced, with refresh triggers for incidents and framework changes.
Does the management body really need specific ICT training?
Yes. Article 5(4) is explicit: members must actively keep up to date the knowledge and skills needed to understand and assess ICT risk, including by following specific training on a regular basis. It is a duty of the members themselves, not something to delegate to the security function.
Do ICT third-party service providers have to join our training?
Where appropriate, yes. Article 13(6) provides for their inclusion in relevant schemes, and Article 30(2)(i) makes the conditions of that participation part of the contractual provisions, so the decision belongs in contract negotiation, not after signature.
Does DORA require certificates?
No. It requires training and, in practice, proof of it. Certificates are one convenient form of proof per person; completion records from your training scheme are the minimum.
Who decides the training budget under DORA?
The management body. Article 5(2)(g) requires it to allocate and periodically review the budget for the entity’s digital operational resilience needs, explicitly including the Article 13(6) awareness programmes and training and ICT skills for all staff.
Can a whole team be trained under one licence?
Yes. Every DORA Academy course, track and the Masterclass can be bought as a team licence from two seats. One manager assigns the seats, follows progress and exam results, and exports a per-person training record; each participant receives a certificate in their own name.